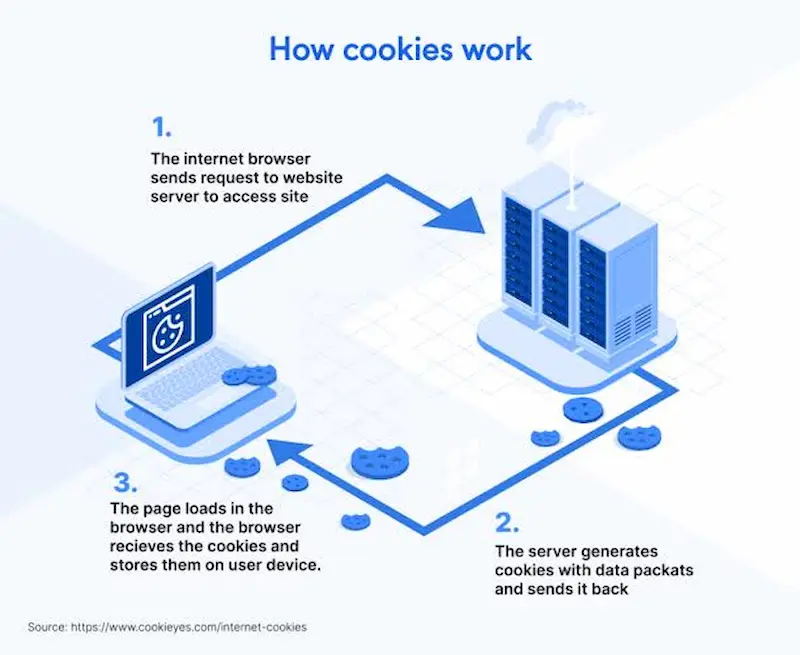
Hidden Web Tools The Complete Browser Data Guide: Cookies, Cache, Local Storage, and When to Clear Them By Alex Morgan on Wednesday, June 3, 2026 Every time a web page takes three extra seconds to load, or a dashboard randomly logs you out right before you hit save, your browser’s internal storage system is usually the culprit. Most people treat browser data like a black box. When something breaks, the universal reflex is to smash the “Clear Browser History” button—wiping out everything—hoping it magically fixes the problem. Sometimes it does. Usually, it just logs you out of every website you care about, resets your preferences, and leaves you wondering why your favorite shopping cart is suddenly empty. To stop playing guessing games with your browser, you have to understand the three distinct ways modern websites squirrel away data on your machine: Cookies, Cache, and Local Storage. 1. Browser Cache: The Local Scrapbook If you open the developer tools in Chrome or Firefox and look under the hood, the cache is usually the largest storage hog by far. What it actually is: Your browser downloads static assets—images, logos, CSS stylesheets, and JavaScript files—the first time you visit a website. Instead of redownloading the company logo every time you click a new page on the same site, your browser pulls it from a local folder on your hard drive. That folder is your cache. How Web Caching Works. Source: KeyCDN Why it breaks things: Web developers push updates constantly. If a developer updates a stylesheet or fixes a script bug, your browser might stubbornly hold onto the old cached version because it thinks it’s saving bandwidth. This leads to broken layouts, missing buttons, or login forms that refuse to submit. When to clear it: When a website looks visually distorted or broken (buttons misaligned, missing icons). When a web app refuses to load a newly updated feature that everyone else is using. When your browser is eating up 50GB of disk space for no apparent reason. 2. Cookies: The Digital Handshake Cookies get a bad reputation in tech news headlines mostly due to third-party ad trackers, but at their core, standard cookies are just tiny text files that websites use to remember who you are. What it actually is: HTTP is a “stateless” protocol. Every time you click a link, the web server treats you like a complete stranger. Cookies are the digital name tags you hand back to the server. When you log into a platform, the site drops an authentication cookie into your browser. For every subsequent click, your browser whispers that cookie back to the server so you stay logged in. Why it breaks things: Cookies expire, get corrupted during failed network handshakes, or clash with privacy extensions. When an authentication cookie gets corrupted, you get trapped in an infinite login loop—where you enter your password, the page refreshes, and it asks you to sign in all over again. When to clear it: When you are stuck in a login loop or a site throws bizarre “session expired” errors seconds after signing in. When you want to completely wipe tracking trackers or reset a site’s preferences back to factory defaults. Warning: Clearing all cookies logs you out of literally every single website you use. Be selective if you can. 3. Local Storage & Session Storage: The Micro-Databases Local storage and session storage are newer, bulkier alternatives to cookies. If cookies are sticky notes, local storage is a filing cabinet. What it actually is: Web apps use local storage to keep massive chunks of data directly inside your browser. If you use a web-based text editor that saves your drafts as you type even when you aren’t connected to the internet, or a dashboard that remembers whether your sidebar is collapsed or expanded, it’s writing that state into your browser’s local storage. Session Storage vanishes the exact second you close that specific browser tab. Local Storage stays there indefinitely until the website’s code explicitly deletes it or you clear your browser data. Why it breaks things: If a web app encounters a bug and writes broken data into your local storage database, the app might freeze on startup, show a blank white screen, or throw cryptic JavaScript errors every time you load the URL. When to clear it: When a web application freezes on a loading spinner or throws persistent JavaScript console errors. When a site’s internal settings or dark-mode toggle get permanently stuck on a broken preference. The Surgical Approach: How to Clear Data Without Nuking Your Browser Stop checking the “All Time” box and wiping your entire browsing history every time an app misbehaves. You can target individual sites with surgical precision. Targeting Specific Browser Data Settings. Source: PCMag How to Clear Data for a Single Site (Chrome/Edge/Firefox): Open the misbehaving website. Click the lock icon or tune icon sitting directly to the left of the URL in your address bar. Click on Site Settings (or “Cookies and site data”). Hit Clear Data or Reset Permissions. Refresh the page. This forces your browser to drop all cached files and cookies for only that specific domain, leaving the rest of your web life untouched. Frequently Asked Questions (FAQs) Q: Does clearing my browser cache delete my saved passwords? A: No. Saved passwords, autofill data, and credit card numbers are stored in a separate, encrypted database managed by your browser’s credential manager. Clearing your cache, cookies, or local storage will not touch your saved passwords unless you explicitly check the box labeled “Passwords” in the clear-data menu. Q: Why do some sites take much longer to load right after I clear my cache? A: That is entirely normal. When you clear your cache, you force your browser to redownload all the images, fonts, and scripts from scratch. Once those assets are pulled down the first time, subsequent page loads will instantly speed back up. Q: Is “Local Storage” a security risk for my computer? A: Generally, no. Local storage is strictly sandboxed by domain name. A website running on example.com cannot read or write to the local storage belonging to bank.com. However, if a site you visit suffers a massive security breach or cross-site scripting (XSS) attack, data stored in local storage can theoretically be exposed, which is why sensitive tokens are sometimes handled via secure, HTTP-only cookies instead. Previous Post Next Post Related Posts Hidden Web Tools Why Two Online Tools Can Give Different Results From the Same File Hidden Web Tools How to Tell Whether a Web Tool Actually Needs the Permissions It Requests Hidden Web Tools Why the Same Website Can Show Different Results on Two Devices